DNS Lookup Tool
Run a free DNS lookup on any domain and see all of its records at once — A, AAAA, MX, TXT, NS, SOA, CNAME, CAA and more — with TTLs, DNSSEC status, and email records (SPF, DKIM, DMARC). Enter a domain, or an IP for a reverse DNS (PTR) lookup.
About DNS Lookup Tool
ToolsPivot's DNS Lookup is a free browser-based tool that queries A, AAAA, CNAME, MX, NS, TXT, SOA, CAA, DS, and DNSKEY records for any domain, and runs a reverse DNS lookup (PTR) when you enter an IP address. You can query Google DNS, Cloudflare, or the domain's own authoritative nameservers. Unlike MxToolbox or HackerTarget, which cap free queries or require accounts for full results, ToolsPivot returns complete DNS data with TTL values and zero sign-up.
How to Use ToolsPivot's DNS Lookup
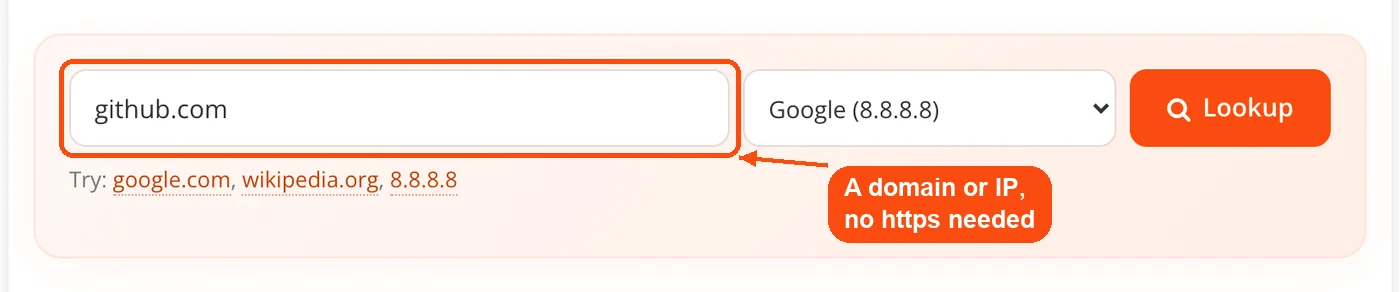
Type your domain: Enter the domain name (like example.com) into the input field. No "https://" or "www" needed.
Choose a DNS server: Query Google (8.8.8.8), Cloudflare (1.1.1.1), or the domain's own authoritative nameservers.
Hit Lookup: One click reads every record type at once: A, AAAA, CNAME, MX, NS, TXT, SOA, CAA, DS and DNSKEY.
Read every record: Each record is listed with its value and TTL (time to live), and the record types the domain does not have are named at the end.
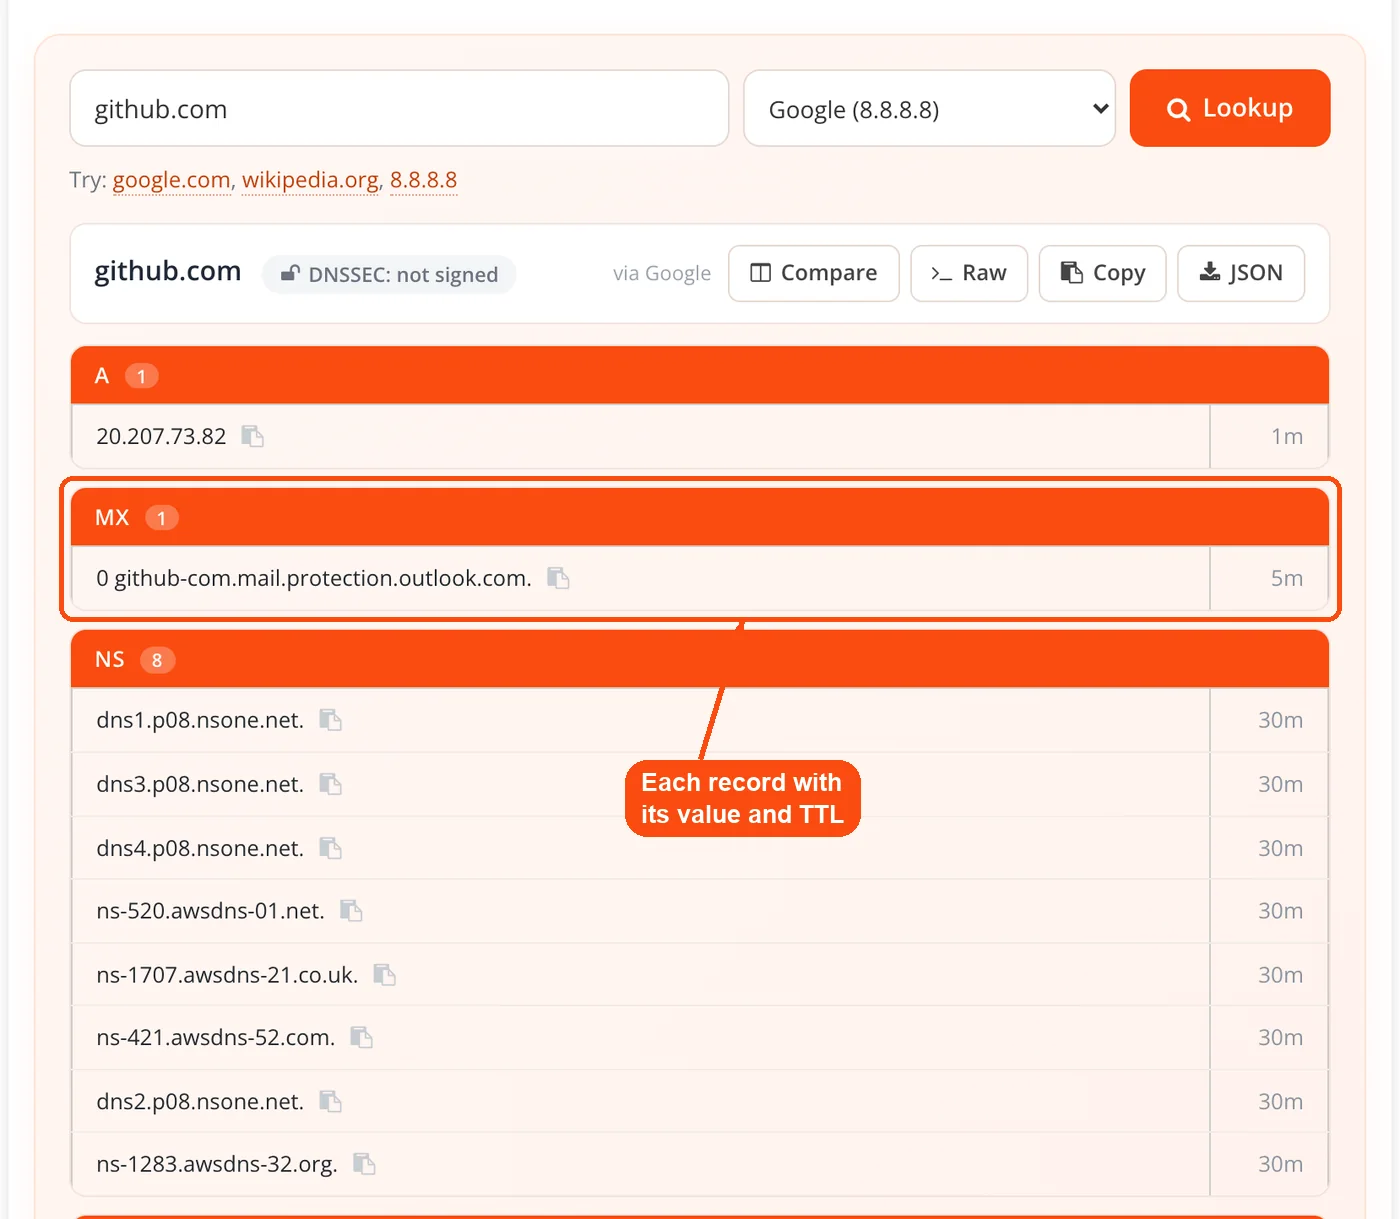
Compare and export: Compare Google and Cloudflare side by side with each record marked as a match or not, see the raw response, copy the records or download them as JSON. The top bar also shows whether the domain is DNSSEC-signed.
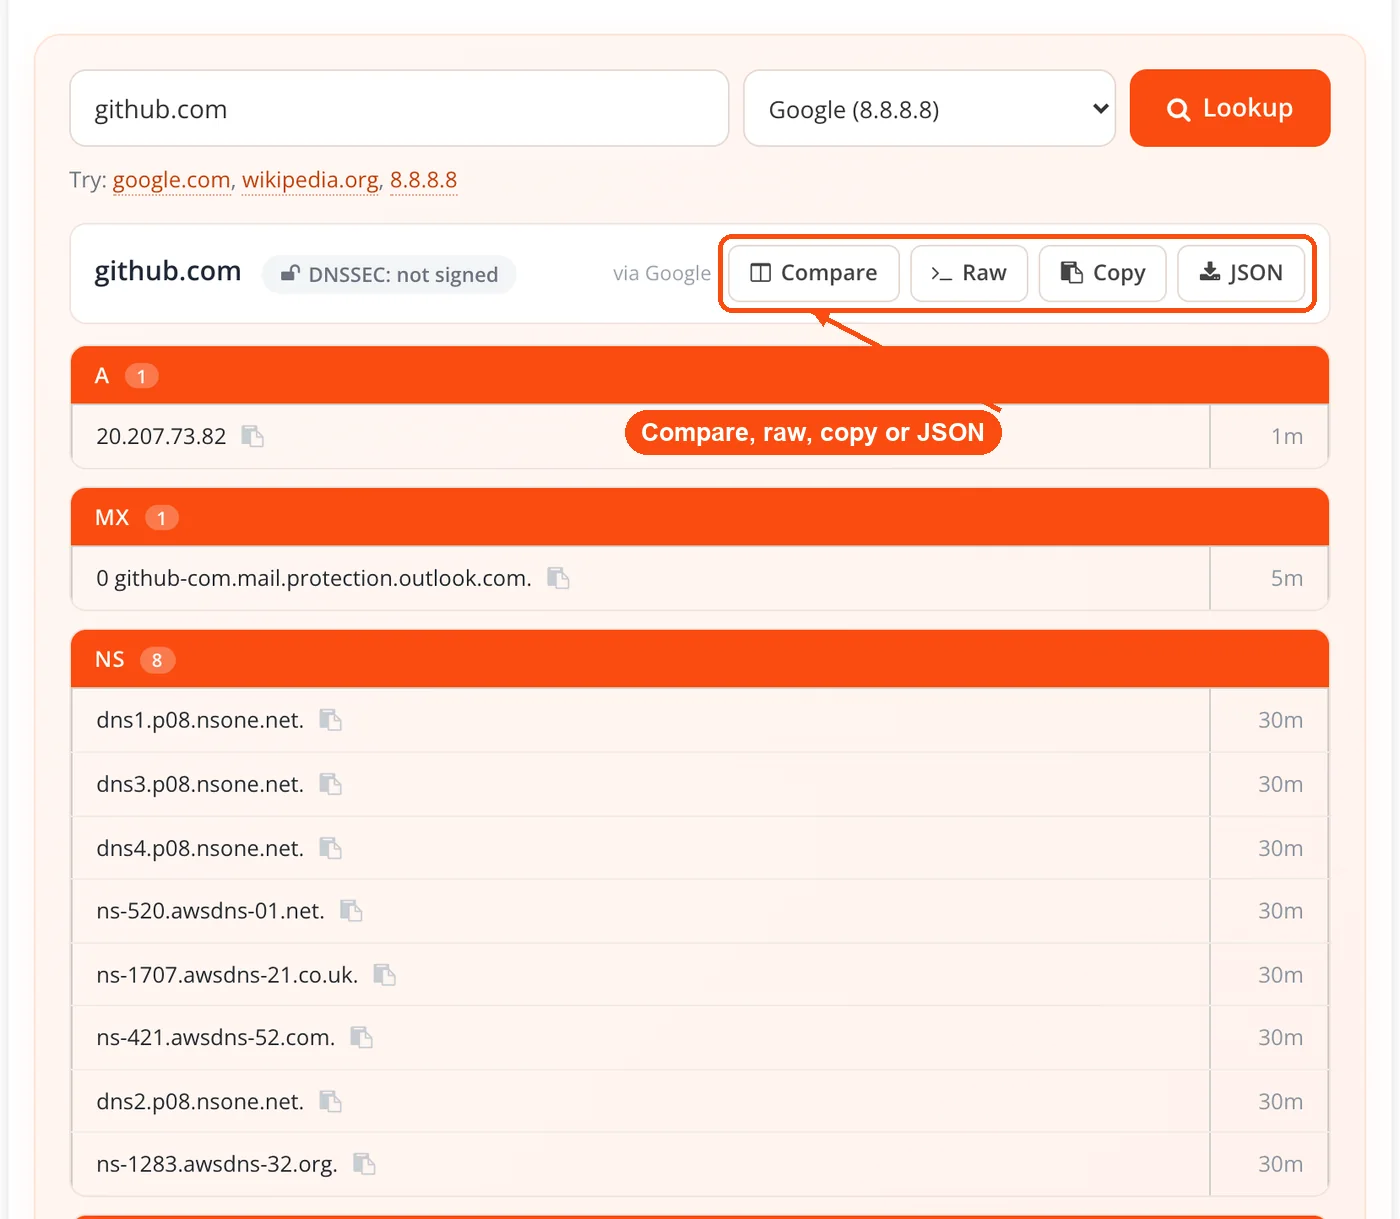
What the DNS Lookup Shows: A, MX, NS, TXT and More
The tool reads 10 DNS record types for a domain, plus PTR records for an IP address. Each one serves a different purpose in how domains route traffic, deliver email, and prove ownership to third-party services. Here's what you can query:
A Record: Maps your domain to an IPv4 address. This is the most basic record, and if it's wrong, your site goes down. Period.
AAAA Record: Same idea as an A record, but for IPv6 addresses. Relevant if your hosting provider supports dual-stack networking.
MX Record: Points to mail servers handling email for the domain, with priority numbers that set the delivery order. A misconfigured MX record is the top cause of bounced emails.
CNAME Record: Creates an alias from one domain to another. You'll see these on subdomains pointing through CDNs like Cloudflare or AWS CloudFront.
NS Record: Lists the authoritative nameservers for the domain. If you just switched hosting providers, this is the first record to check. Compare the DNS lookup name server entries with the ones your registrar shows: if they differ, the change has not taken effect yet.
TXT Record: Stores text strings used for SPF, DKIM, DMARC, Google Search Console verification, and other service integrations. One domain can have dozens of TXT records.
SOA Record: Contains zone administration data: primary nameserver, admin email, serial number, and refresh intervals. Useful for debugging propagation timing.
PTR Record: Used for a reverse DNS lookup. What is reverse DNS lookup in practice? Instead of translating a domain to an IP, it translates an IP back to a hostname. Enter an IPv4 or IPv6 address instead of a domain and the tool runs an IP DNS lookup that returns its PTR record. Email servers use PTR records to verify sender legitimacy.
CAA Record: Defines which Certificate Authorities can issue SSL/TLS certificates for the domain. Missing CAA records don't break anything, but having them tightens security.
DS Record: Part of the DNSSEC chain of trust. It links a child zone to its parent zone's signing key.
DNSKEY Record: Holds the public keys used in DNSSEC validation, including the Zone Signing Key (ZSK) and Key Signing Key (KSK).
Why Use ToolsPivot's DNS Lookup
No account required: Run unlimited DNS queries without creating a login. Most alternatives (MxToolbox, HackerTarget) restrict free users to a daily cap or limited record types.
11 record types in one place: Query everything from A records to DNSKEY records without switching between separate tools for each type.
Multi-resolver comparison: Check the same domain against Google DNS, Cloudflare, and the authoritative server, or compare Google and Cloudflare side by side. This is the fastest way to spot propagation inconsistencies after a DNS change.
TTL visibility at a glance: Every result includes time-to-live values in seconds, so you know exactly when cached records will expire and new ones will take effect.
Pairs with other checks: Combine DNS results with a server status check or page speed test to get a full picture of domain health before or after migrations.
Works on any device: As an online DNS lookup tool, it works in any browser. No need to install dig, nslookup, or any command-line utility on your laptop or phone.
Instant results: Most queries return structured data in under 3 seconds, compared to the manual process of running separate dig commands per record type.
Reading Your DNS Results
The output table shows three columns for each record: type, value, and TTL. Knowing what to look for in each column saves you from misreading a perfectly normal result as an error.
A and AAAA values should contain IP addresses that match your current hosting server. If the DNS lookup A record result shows an IP you don't recognize, your domain might still be pointing to an old host. Cross-reference the IP with your IP address lookup to confirm.
MX records show a priority number followed by a mail server hostname. Lower numbers mean higher priority. If you use Google Workspace, you should see entries like ASPMX.L.GOOGLE.COM with priority 1. For Microsoft 365, look for something ending in .mail.protection.outlook.com.
TXT records can look chaotic because domains pile up verification strings from multiple services. Look for "v=spf1" (your SPF policy), "v=DKIM1" (email signing), and "v=DMARC1" (email authentication policy). If you're missing any of these and you send email from the domain, that's a problem worth fixing.
TTL values are expressed in seconds. A TTL of 3600 means DNS resolvers cache that record for one hour. Before making DNS changes, lower your TTL to 300 (5 minutes) at least 24 hours in advance. This way, when you flip the record, the old cached version expires quickly across global resolvers.
Situations Where a DNS Lookup Pays Off
After switching hosting providers
You've migrated a WordPress site to a new server. The site loads fine from your office, but a client in another city still sees the old version. Run a DNS lookup against multiple resolvers to check whether the A record has propagated to Google DNS and Cloudflare. If one resolver still returns the old IP, that region hasn't caught up yet. Checking the TTL tells you how long to wait.
Diagnosing bounced emails
Your marketing team's Mailchimp campaigns are landing in spam. Run a DNS lookup: MX and TXT records show whether your SPF record includes Mailchimp's sending servers. A missing "include:servers.mcsv.net" entry in the SPF string is one of the most common causes. Run the lookup, spot the gap, update the TXT record, and validate recipient addresses before the next send.
Preparing a domain purchase
Before buying a domain on a marketplace, run a DNS lookup for domain records to check its configuration. Query the A record to see where it points. Look at MX records to check if it's actively handling email. Use ToolsPivot's WHOIS lookup and domain age checker alongside the DNS results to build a full picture of the domain's history and current state.
Auditing DNSSEC configuration
If your registrar says DNSSEC is active, verify it. Query DS and DNSKEY records through ToolsPivot. If both return valid data and the key tags match between the DS and DNSKEY records, the chain of trust is intact. Empty results mean DNSSEC isn't configured, even if the registrar dashboard says otherwise.
Verifying CDN setup
You've configured Cloudflare or AWS CloudFront for a subdomain. Query the CNAME record for that subdomain. If it points to the CDN provider's hostname (like d1234.cloudfront.net), the setup is correct. If it still shows an A record with a direct IP, the CDN isn't active for that subdomain.
DNS Lookup vs. DNS Propagation Check
These two tools solve different problems, and mixing them up wastes time. A DNS lookup queries one specific resolver and returns whatever records that server holds right now. A propagation checker queries dozens of servers worldwide and shows you whether they all agree.
Use ToolsPivot's DNS Lookup when you need to inspect the actual record values, types, and TTLs for a domain. Use a propagation tool when you've already made a change and want to track how far it has spread. Think of the lookup as a magnifying glass (deep detail, one source) and propagation as a satellite view (broad coverage, less detail). If your website ping test shows the site is reachable but slow, the DNS lookup can confirm whether the A record is pointing to the right server.
Quick Answers About DNS Lookup
A DNS lookup queries a Domain Name System server to retrieve records associated with a domain name. These records include IP addresses (A/AAAA), mail server routes (MX), nameserver delegations (NS), and text-based authentication strings (TXT). The process translates human-readable domain names into machine-readable data that browsers and servers need to communicate.
Yes, 100% free with no daily query limits and no account required. You get full access to all 11 record types and all 3 resolver options without paying or signing up.
A reverse DNS lookup starts from an IP address and asks which hostname it belongs to, the opposite of a normal DNS lookup. The answer lives in a PTR record that the owner of the IP block publishes. Mail servers rely on it heavily: a sending IP with no PTR record, or one that does not match the sending domain, is a common reason email gets rejected or marked as spam.
Type the IPv4 or IPv6 address into the box instead of a domain and click Lookup. The tool converts it to the reverse lookup name (in-addr.arpa or ip6.arpa) and returns the PTR record, or tells you plainly when the IP has none. If the PTR record is missing or wrong, the fix has to come from whoever controls the IP, usually your hosting provider or ISP.
On Windows, macOS, or Linux, run nslookup followed by the IP address, for example nslookup 8.8.8.8. On macOS and Linux, dig -x 8.8.8.8 returns the PTR record with its TTL, and host 8.8.8.8 gives a one-line answer. These read the same PTR record this page looks up, so use whichever is closer to hand.
DNS changes typically propagate within 24 to 48 hours, though many records update globally in under 4 hours. The speed depends on TTL values set on the old records. Lower TTLs mean faster propagation because resolvers discard cached data sooner.
You can look up DNS records for any publicly registered domain. DNS is a public system by design, so querying records for google.com, your competitor's site, or a domain you're thinking about buying is completely normal and allowed.
Nslookup is a command-line program built into Windows and macOS. ToolsPivot's DNS Lookup does the same thing but runs in your browser, supports more record types from a single interface, and queries multiple resolvers without typing separate commands for each one.
Different DNS resolvers cache records independently based on TTL values. After a DNS change, some servers still hold the old cached version while others have already fetched the updated record. This gap closes as TTLs expire across all resolvers, usually within 48 hours.
NXDOMAIN stands for "Non-Existent Domain." It means the queried domain name doesn't exist in the DNS system. Common causes include typos in the domain name, an expired domain registration, or a domain that was never registered in the first place.
Query the TXT records for your domain using ToolsPivot's DNS Lookup. Look for an entry starting with "v=spf1" followed by the IP addresses or "include" directives for every service you send email from (Google Workspace, Mailchimp, SendGrid, etc.). If a sending service is missing from this list, its emails may fail SPF checks.
No. A domain availability check tells you whether a domain name is registered or open for purchase. A DNS lookup queries the actual records configured for an already-registered domain. They answer different questions entirely.
Not directly, but misconfigured DNS causes problems that hurt rankings. Wrong A records cause downtime, which tanks crawl rates. Missing or broken CNAME records prevent CDN delivery, slowing page load speed. Bad MX or TXT records don't affect rankings, but they'll wreck your email deliverability. Use the DNS lookup alongside a full SEO check to cover both sides.
No. Queries are processed in real time and not logged or stored on ToolsPivot's servers. Your lookup history stays private.
Log into your domain registrar or DNS hosting provider (like Cloudflare, Namecheap, or GoDaddy) and update the incorrect records from there. ToolsPivot's DNS Lookup is a read-only diagnostic tool. It shows you what's configured but doesn't modify records. After making changes, run another lookup to confirm the update took effect. You can also check your domain blacklist status if email deliverability problems persist after fixing DNS.


